How to handle sensitive information in the hiring process
A practical guide for hiring teams on collecting, storing, sharing and deleting candidate data safely and legally at every stage of hiring.
Sensitive information in the hiring process is any candidate data that could harm the person or expose your company if it leaks or is misused. That includes ID and tax numbers, health and disability details, background check results, salary history, diversity data, and the recordings and scores your assessments produce. Every hiring team holds this data, usually across more tools than anyone has mapped. The best practices below are about recruiting while respecting privacy: fair to candidates and defensible if a regulator asks.
 ChatGPT
 Gemini
 Claude
 Grok
 Perplexity
TL;DR
- Sensitive hiring data is candidate data that could harm the person or expose you if leaked, such as IDs, health details, and background checks.
- Ask for each item at the latest point you need it. Collect ID, bank, and tax data only after an offer, never by email.
- Never ask about health, disability, or medical history before a conditional offer, per the EEOC. Avoid protected traits at every stage.
- IBM's Cost of a Data Breach Report 2026 puts the global average breach at $4.99 million, a 12% rise and a record high.
- Most leaks come from copies in inboxes, note docs, chat threads, and CSV exports, not the ATS. Map every place data lands.
- Set a retention period per country and automate deletion. US federal rules require keeping hiring records for 1 year.
- Before data reaches a vendor, ask for SOC 2 Type II, ISO 27001, a data processing agreement, and, for AI tools, a bias audit.
What counts as sensitive information in the hiring process?
Sensitive information in the hiring process falls into three groups: data that identifies a person and can be used for fraud, data the law treats as special, and data your process creates about the candidate.
A CV with a name and email is personal data; a passport scan, a health disclosure, or a webcam recording is sensitive and needs tighter rules.
Type of data | Examples | Where it shows up | Rule of thumb |
|---|---|---|---|
Identity and financial | Passport or ID scans, Social Security or National Insurance number, bank details, tax forms | Right-to-work checks, onboarding | Collect only after an offer, never by email |
Special category | Health, disability, pregnancy, religion, sexual orientation, ethnicity, union membership | Accommodation requests, diversity surveys, interview small talk | Keep apart from hiring decisions |
Criminal and credit history | Background check reports, credit reports, driving records | Pre-employment vetting | Written consent first, limited access |
Compensation | Current salary, salary history, expectations | Screening calls, offer stage | Check local salary history bans |
Assessment and interview data | Test scores, video and audio recordings, webcam snapshots, AI-generated notes | Skills tests, AI interviews, panel interviews | Tie to job criteria, set a deletion date |
Third-party data | Reference comments, social media findings | Reference checks, sourcing | Record only what is job-related |
The UK Information Commissioner's Office makes the same point in its draft recruitment guidance: employers and recruiters often handle health, diversity and criminal conviction data during hiring, and these need extra care. Our confidentiality agreement entry explains how to put the obligations of your hiring team in writing.
Why does protecting candidate data matter in 2026?
Protecting candidate data matters more in 2026 because hiring now runs through more systems, attracts more fraud, and sits under more regulators than it did a few years ago. A single leaked export of applicant IDs or recordings hurts the candidates, the employer brand, and, increasingly, the legal budget.
Three numbers show the pressure:
- Breach cost: IBM's Cost of a Data Breach Report 2026 puts the global average breach at $4.99 million, a 12% rise on the year before and a record high.
- Candidate fraud: Gartner predicts that by 2028, 1 in 4 candidate profiles worldwide could be fake. In its 2025 survey of 3,000 job candidates, 6% admitted to interview fraud, either posing as someone else or having someone pose as them. Teams respond with ID checks and proctoring, which means they now hold more sensitive data, not less.
- Trust: the same Gartner research found that only about a quarter of candidates trust AI to evaluate them fairly. Careless handling of their data makes that worse.
Regulators are also looking at applicant data directly. In July 2023, California's Attorney General sent inquiry letters to large employers asking how they comply with the CCPA for employees and job applicants, whose data has been covered since January 1, 2023.
Which laws cover candidate data?
Candidate data is covered by privacy laws, employment laws, and, more and more, AI laws. Which ones apply depends on where the candidate lives, not only where your company sits. A US company hiring in Berlin is under GDPR for that candidate.
Law or rule | Where | What it means for hiring |
|---|---|---|
GDPR and UK GDPR | EU, EEA, UK | Lawful basis, privacy notice at collection, data minimisation, set retention, candidate rights to access and erasure, breach reports |
CCPA as amended by CPRA | California | Applicants have consumer privacy rights, including notice at collection and the right to know and delete |
ADA, enforced by the EEOC | US | No disability-related questions or medical exams before a conditional offer |
Fair Credit Reporting Act | US | Standalone disclosure and written consent before a background check, plus adverse action notices |
NYC Local Law 144 | New York City | Automated hiring tools need a bias audit within one year before use, public results and candidate notice |
EU AI Act | EU | AI used to screen applications or evaluate candidates is classed as high-risk |
None of this replaces legal advice, and state, provincial, and country rules add detail. The practical step is to keep a hiring compliance checklist for each country you hire in and review it once a year.
How should you handle sensitive information in the hiring process at each stage?
Handling sensitive information in the hiring process works best stage by stage, because each stage collects different data. The rule is to ask for each item at the latest point you need it, show it only to the people who need it, and know where it goes after the decision.
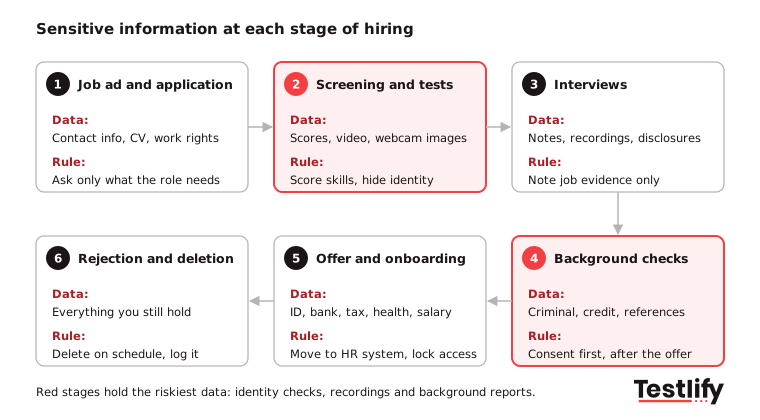
- Job ad and application: Ask for contact details, the CV, and the right to work only. Link your applicant privacy notice on the form itself. Skip date of birth, photos, marital status, and full home address.
- Screening and assessments: Score skills, not identity. Reviewers can see results with names hidden; our guide to blind hiring shows how. Tell candidates when tests use webcam snapshots or recordings, and why.
- Interviews: Use a structured scorecard and write down job evidence only. If the interview is recorded or AI-scored, say so before it starts.
- Background checks and references: Run them after a conditional offer, for the finalist only. In the US, the FTC's guidance for employers requires a standalone written disclosure, written permission, and a copy of the report before any rejection based on it. See our overview of background checks.
- Offer and onboarding: Collect ID, bank, tax, and benefits data inside the HRIS or payroll tool, not by email or chat. Move the hired candidate's file out of the recruiting tools.
- Rejection and deletion: Delete or anonymize rejected candidates' data on a fixed schedule, including spreadsheets, downloads, and shared links.
Pro tip: Map every place candidate data lands, not only the ATS. In our experience, the leaks rarely come from the core system. Across the teams we work with, the copies sit in inboxes, interview note docs, chat threads and CSV exports that nobody owns.
What should you never ask candidates before a job offer?
Employers should never ask candidates about health, disability, or medical history before a conditional job offer and should avoid questions about any protected trait at any stage. The EEOC's pre-employment guidance says this holds even if you plan to read the answers only after the offer.
Keep these off application forms and out of interviews:
- Health conditions, medication, past illnesses, sick days taken, or workers' compensation claims
- Pregnancy, plans to have children, childcare, or marital status
- Age or date of birth, unless a legal minimum age applies to the role
- Religion, national origin, citizenship (ask about the right to work instead), race or ethnicity
- Arrest records, and in many US states and cities, any criminal history before an offer
- Salary history, which a growing list of US states and cities ban
What you can ask: whether the candidate can perform the essential tasks of the job, with or without reasonable accommodation. Diversity data for reporting is collected on a separate, voluntary form that hiring managers never see.
How should you store, share, and secure candidate data?
Candidate data should live in as few systems as possible, with access limited to the people who need it for the current hiring decision. A secure ATS or assessment platform beats any mix of email attachments, shared drives, and personal notes.
- One home per data type: Applications in the ATS, assessments in the assessment platform, offer and ID data in the HRIS. No copies in personal folders.
- Role-based access: Hiring managers see their own requisitions. Only HR sees background reports and accommodation requests.
- Strong sign-in: Single sign-on and two-factor authentication on every hiring tool, with access removed the day someone leaves the team.
- Encryption: Data encrypted in transit and at rest, which should be standard in any vendor you use.
- Safe sharing: Share expiring links from the platform instead of attaching CVs or reports to email. Never send ID documents over chat apps.
- Training: Recruiters and interviewers learn what not to write down, how to spot phishing aimed at hiring teams, and who to call when something goes wrong.
For a deeper look at the technical controls, read our guide to candidate data security.
How long should you keep candidate records?
Candidate records should be kept for the shortest period the law and your process require, then deleted on schedule. There is no single global number, so set a retention period per country, write it in your privacy notice, and automate the deletion.
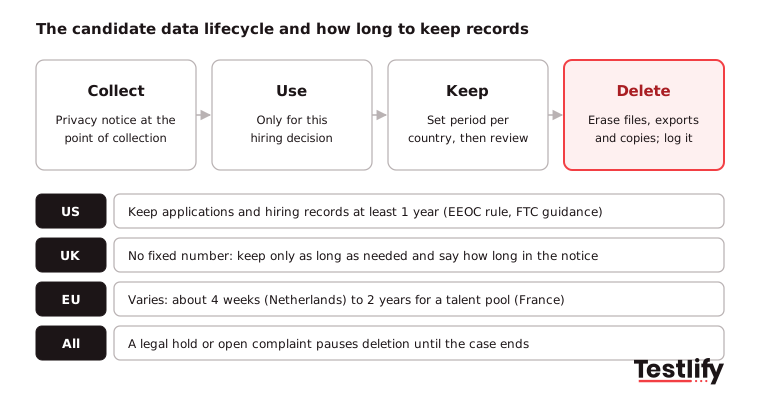
- United States: Federal rules require employers to keep applications and hiring records for 1 year from when they were made or the hiring decision, whichever is later, and 2 years for some public employers and federal contractors, as the FTC's employer guidance notes. A discrimination charge means keeping everything until the case ends.
- United Kingdom: UK GDPR sets no fixed number. Keep data only as long as you need it for the hiring decision and possible legal claims, and state the period in your privacy notice.
- European Union: National regulators differ. According to Recruitee's 2026 GDPR guide, the Dutch regulator expects unsuccessful applicants' data to be deleted within about four weeks, while France's CNIL allows a talent pool of up to two years in some cases.
If you want to keep rejected candidates for future roles, ask for their consent with a clear end date, and ask again before it runs out.
How do you handle sensitive disclosures in interviews?
Interviewers should handle a sensitive disclosure by acknowledging it briefly, steering back to job-related questions, and leaving it out of their notes and scores. Candidates often mention health, family or religion without being asked, and that information must not shape the decision.
- Do not probe: "Thanks for sharing. Let's go back to the project you mentioned" is enough.
- Do not record it: Keep scorecards to evidence against the agreed criteria. If an AI note-taker captured the comment, remove it from the transcript.
- Route accommodation requests to HR: A candidate who asks for extra time on a test or a different interview format should get a quick, private answer from HR, not from the panel.
- Train and escalate: Give interviewers a short script and a named HR contact for borderline cases.
Structured interviews make this easier because every candidate answers the same job-related questions and gets scored on the same criteria.
How do you check vendors and AI tools that touch candidate data?
Hiring teams should check every vendor that stores or processes candidate data before any data reaches it: ATS, assessment platform, video interview tool, background check provider and any AI add-on. Under GDPR you stay responsible for what your vendors do with candidate data.
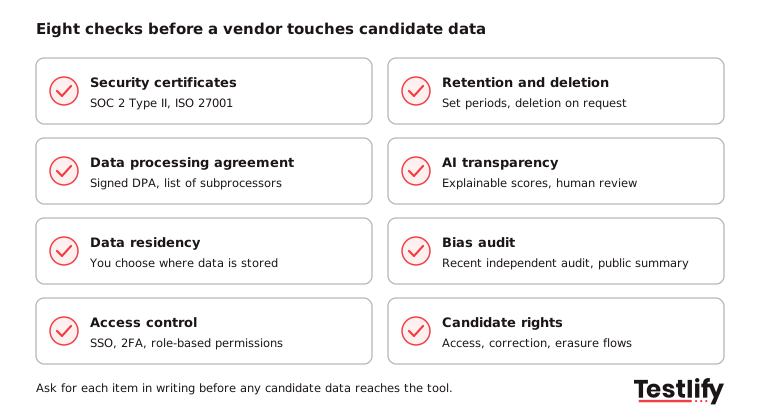
Ask each vendor for:
- Current security certificates, such as SOC 2 Type II and ISO 27001.
- A signed data processing agreement and a list of subprocessors.
- A choice of where candidate data is stored.
- Single sign-on, two-factor authentication and role-based permissions.
- Retention settings and deletion on request.
- Clear explanations of how AI scores are produced, with a person reviewing decisions.
- A recent independent bias audit, if the tool ranks or scores candidates.
- A simple way to answer candidates' access and erasure requests.
AI tools carry extra weight. The EU AI Act lists AI used for recruitment or selection, including screening applications and evaluating candidates, as high-risk, with duties on documentation, human oversight and transparency. In New York City, Local Law 144 already requires a bias audit within one year before use and notice to candidates 10 business days before an automated tool is used.
What should you do if candidate data is breached?
A recruiting team that suffers a breach should contain it, assess the risk to candidates, notify regulators and people when required, and fix the cause. Speed matters: under UK GDPR, the ICO expects a report as soon as possible and, where feasible, within 72 hours.
- Contain: Revoke the shared link, reset the account, recall the email, or cut the vendor's access.
- Assess: Work out whose data was exposed, what kind, and how sensitive it is. ID scans and background reports raise the risk sharply.
- Notify: Report to the regulator within the deadline where the law requires it, and tell affected candidates without undue delay when the risk to them is high. US state breach laws set their own rules.
- Support candidates: Tell them what happened, what data was involved and what they should watch for, such as fake recruiter messages using their details.
- Fix and record: Close the gap, update training, and keep a written record of the breach and your response.
How does Testlify protect candidate data in assessments?
Testlify protects candidate data with certified security, privacy controls and fair-hiring checks built into the assessment platform. Assessments are often where hiring teams collect the most sensitive data, such as recordings and webcam images, so the platform is designed to keep that data contained.
- Certified security: ISO 27001 and SOC 2 Type II, with penetration testing and details on the Testlify trust center.
- Privacy compliance: GDPR, CCPA and the Data Privacy Framework, with a data processing agreement and regional data residency, so you choose where candidate data is stored. See GDPR compliance.
- Access control: Role-based access, plus SAML SSO and two-factor authentication.
- Fair scoring: Automated scoring against the same criteria for every candidate, with explainable results and human oversight. Testlify's matching model completed a third-party NYC Local Law 144 bias audit on June 16, 2023.
- Integrity without extra collection: 20+ proctoring checks, including tab tracking, webcam snapshots and AI assistance detection. See anti-cheating and proctoring.
- Fewer copies: Two-way sync with 100+ ATS and HRIS tools, so results flow into your ATS instead of through email and spreadsheets.
Testlify has 3,500+ validated tests for tech and non-tech roles. You can start a 7-day free trial with no credit card, or book a demo to review the security setup with the team.
Key takeaway: Handle sensitive information in the hiring process by collecting less, asking later, limiting who sees it, and deleting it on schedule. Most risk sits in the copies and the vendors, so map both before the next hiring push.
Frequently asked questions (FAQs)
Wordpress Developer
Yash Patel is a Wordpress and SEO Specialist at Testlify with 3+ years of experience in technical SEO, on-page optimization, and content strategy. He works on improving Testlify's organic presence and produces content focused on hiring, talent assessment, and HR technology.
LinkedInRelated resources
View all
Hiring Guide
Direct vs indirect hiring costs: A complete breakdown
Hiring Guide
Building a strong employer brand with visual storytelling
Hiring Guide
The employer’s guide to hiring seasonal international workers
Hiring Guide
Grey collar jobs: what they are, examples, and how to hire [2026]
Hiring Guide
6 Stages of the performance management cycle
Hiring Guide
Recruitment vs talent acquisition: Key differences
Get started.
Hire on proof, not resumes.
Run your first skills-based assessment free — no credit card required.